LEAF Verified is Wavelynx's next-generation access credential, delivering public-key security at the chip level. No key management. Simplified interoperability. High-level security that scales to zero trust for enterprises that need it.
Legacy credentials broadcast the same static number on every tap. That code can be easily copied by $20 cloning devices and replayed forever. See just how easy it is to clone a legacy credential in this short video.
LEAF Verified stores its private key directly in the chip's secure hardware. It's never transmitted, never remotely extractable. Every tap generates a unique proof that expires the moment it's used.
Two EAL 6+ ratings, built to work across a multitude of systems.
Public-key security provisioned at the wafer. Ships in ISO card and key fob form factors, ready to use out of the box.
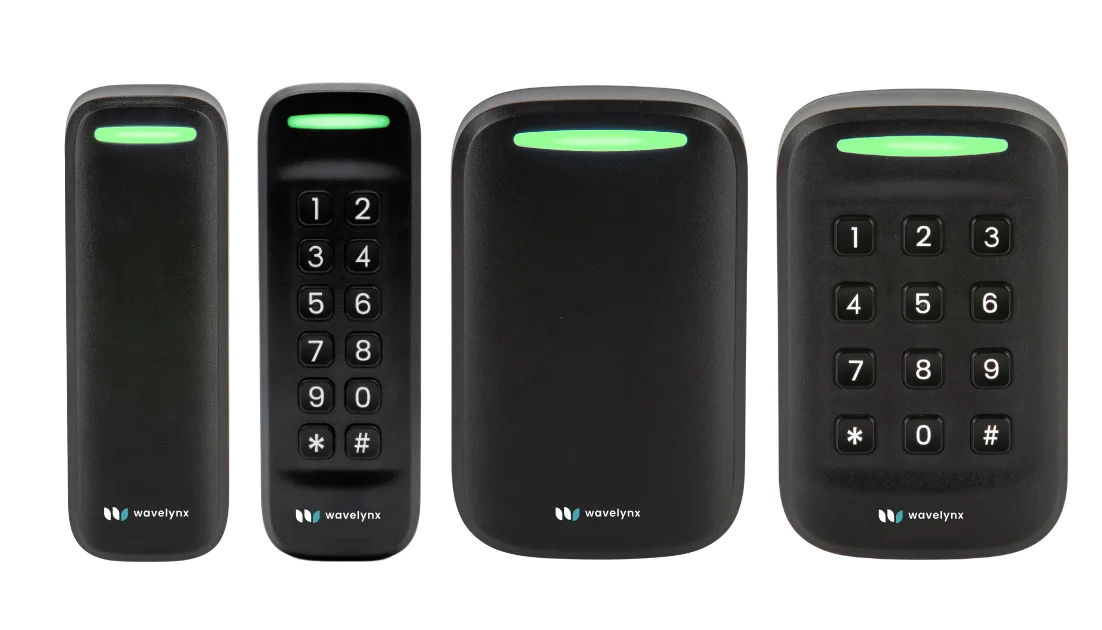
Drops into your existing infrastructure. Reads legacy and modern credentials side by side, so you transition on your schedule, not anyone else's.
The access control industry has run on the same model for decades. Here's what changes when you stop.
Built on open standards and the LEAF Community ecosystem. LEAF Verified makes it easy for any vendor to add compatibility. As long as the device is capable of the encryption (any modern reader should be), LEAF Verified can work with it.
One credential across every vendor in your stack.
Make your Verified credentials dual-tech by adding 125 kHz prox so you can transition readers at your own pace. Start with the most vulnerable areas first. We make your path to modernization flexible from day one.
Protect your hardware investments while upgrading your security.
We share more than our competitors. LEAF Verified is built on standard, well-understood cryptography. No proprietary protocols. Wavelynx maintains an open-source library for the LEAF Community so any device manufacturer can add support.
Show your board exactly how the security works. No black boxes.
Every LEAF Verified credential ships with both tiers built in. Your reader policy decides which one runs, door by door.
One-Way Proof · Zero Key Management
The default. Mount the reader. Walk away. It works. The credential proves itself to the reader without anyone handing out secrets, ideal for base building systems shared across an enterprise or property.
Two-Way Trust · Enterprise PKI Ready
Credential and reader verify each other. Bring your own PKI to extend the same trust chain across your entire ecosystem, physical and mobile Aliro credentials alike.
Every LEAF Verified credential has native NFC. Tap it to any phone and your access control platform decides what happens next. The first use case: self-enrollment that eliminates manual data entry entirely.
The tap experience is powered by your access control platform. Wavelynx provides the NFC capability on every credential. Ask your PACS or PIAM provider about LEAF Verified integration.
Every credential pack ships with a QR code linked to a downloadable badge list. Scan it, import hundreds of badges in seconds.
Start with a conversation, prove it in your environment, and scale at your own pace.
We'll ship a sample pack to your desk. Hold the credential, see the form factors, and share them with your team to start the conversation.
We'll assess your infrastructure, map an upgrade path, and provide a pilot pack with credentials and a reader to test in your environment.
Roll out building by building on your schedule. Legacy and LEAF Verified credentials work side by side during the transition, so nothing goes dark while you upgrade.
Tell us about your environment and we will send physical credentials to test, plus a phased upgrade plan from our engineers that fits your budget and timeline.
We reply within 1 to 2 business days.
Possibly not. LEAF Verified requires a reader with public-key (ECC) support. Today that means Wavelynx APEX, with more devices being added. Newer readers may only need a firmware update, while older hardware will need replacement. To see where your fleet stands, check the device compatibility matrix.
Nothing. Open application mode works out of the box with zero key management. No SAM cards, no key ceremonies, no secret distribution. When you're ready for mutual authentication, you can layer on enterprise PKI at your own pace. It's there when you need it, not before.
No. LEAF Verified is built on open standards and open-source cryptography. Any reader, panel, or platform manufacturer can add support. The growing LEAF Community ecosystem already includes hardware and software from multiple vendors. The credential works the same regardless of whose reader is on the wall.
The infrastructure you deploy for LEAF Verified today is already built for it. Wavelynx Wallet brings the same public-key model to phone wallets using the Aliro standard from Apple and Google. Same trust chain, physical and mobile.
Both sides verify. The credential proves itself to the reader. The reader proves itself to the credential. Nobody gets access until both checks pass. It's the same model your IT team already uses for network access, applied to physical doors.


Custom key ownership: a dedicated AES key profile exclusive to your organization. Standalone or encoded onto LEAF Verified.
Learn morePre-configured symmetric smart credentials. Any LEAF-compatible reader, no key setup.
Learn more