Whether you need stronger security, flexibility, or to transition from legacy tech, a modern system starts with the credential. Our credential solutions give you a clear path to modern security, on a flexible timeline that works for you.
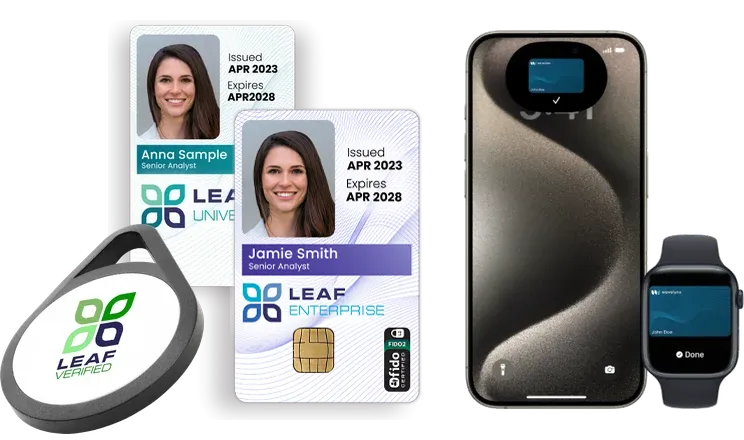
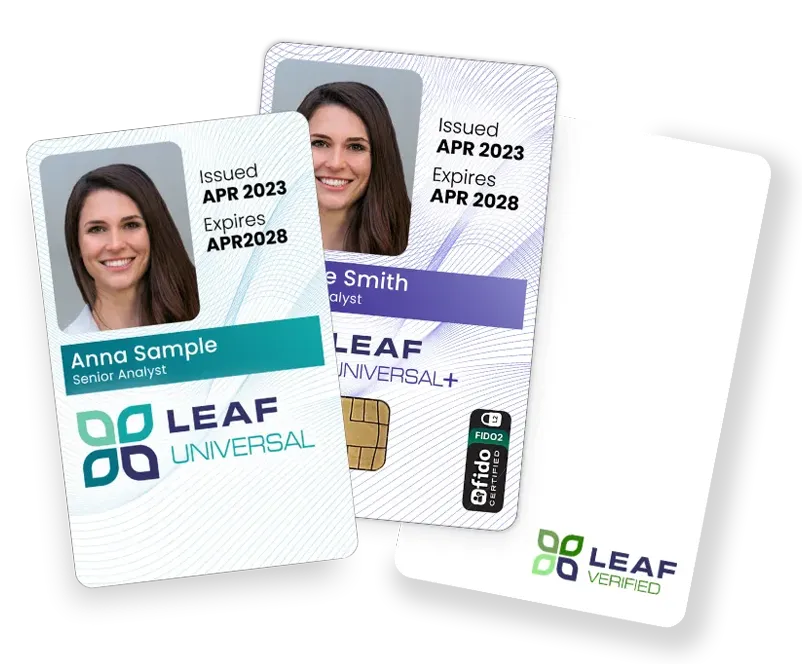
The LEAF open standard means any manufacturer can make our credentials compatible with their devices. LEAF invites it. LEAF shares the technical specs freely, so a growing ecosystem of partners can build on it. That gives you flexibility in an industry that too often locks you into one vendor's system.
Our credential solutions use NXP MIFARE® secure chips, the same technology trusted globally for contactless payments and secure transactions. An NXP chip is like having a tiny bank vault securing your employee badge.
Every environment has different security needs. The Wavelynx portfolio, based on the LEAF standard, provides a clear roadmap to step up your security without changing your reader base.
Wavelynx's next-generation public-key credential. Enterprise-grade security with no key management, simplified interoperability, and scalability into zero-trust environments.
Control your keys and how your cards are set up, without getting locked into one vendor's system. Wavelynx handles the complex parts (key creation, protection, and management) at no extra cost.
Skip the complexity. LEAF Universal is a highly secure credential that works with a community of devices out of the box. No setup, no configuration, no waiting.
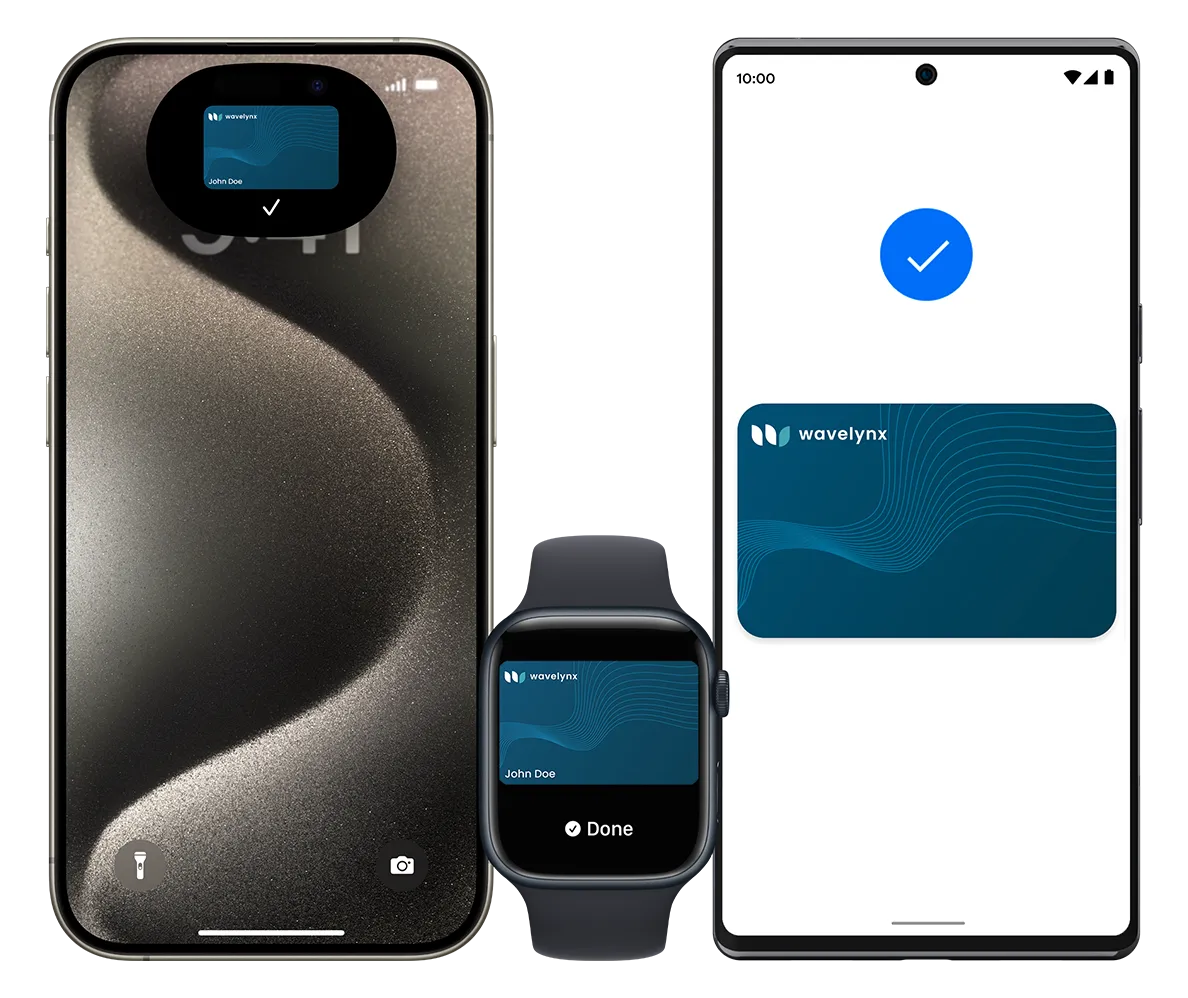
Nothing to lose, nothing to forget at home. The same secure access you rely on, on the phone already in your pocket.
Most organizations hand each employee two to five different credentials. Stop the complexity of issuing, managing, and revoking multiple credentials by converging what you need onto one card.
Passwordless, phishing-resistant login to Windows, Mac and your identity provider. Tap the badge, skip the password.
See FIDO2Secure long-range reads for vehicle gates and for tracking people and assets across a warehouse floor.
See UHF125 kHz Prox and a magstripe on the same card, so legacy readers keep working while you move to modern credentials.
See legacy supportEvery vendor claims openness. Here is how Wavelynx actually delivers it, and why it matters to your bottom line.
Your badge works on any compatible reader, not just ours.
Backed by a multi-vendor ecosystem, your infrastructure investment isn't tied to one company's roadmap.
See the device compatibility matrixYour keys, your rules. Upgrade on your timeline.
When key models change, you upgrade keys, not the hardware.
See how key ownership worksBuilt on NXP MIFARE: billions of credentials deployed worldwide.
Standardized cryptography on a global platform trusted by transit and governments. No black boxes.
Our engineers will design a phased credential upgrade plan that works with your environment, budget, and timeline.
LEAF is an open-standard cryptographic format for physical access credentials, governed by the LEAF Community. It was created to break vendor lock-in by enabling multiple reader manufacturers to decrypt the same secure card format. Wavelynx credentials are built strictly on the LEAF standard.
Universal is the plug-and-play symmetric credential: secure out-of-the-box for organizations that want simplicity. Verified is our flagship credential: a public-key credential that's just as easy to deploy but built to resist cloning, and it can carry existing MIFARE applications and custom key sets on the same card. Enterprise is the key-ownership option: a dedicated symmetric key profile exclusive to your organization, available standalone or on a Verified credential.
Not necessarily. Dual-technology cards contain legacy 125 kHz Prox technology so they work with your existing readers. As you replace old readers with modern smart-capable readers (like Wavelynx APEX or Ethos), those doors will read the high-security smart chip instead. You can transition door-by-door without ever leaving employees without access.
Yes. Wavelynx Wallet supports NFC mobile credentials loaded into Apple Wallet or Google Wallet. We also actively support the Aliro mobile credential standard developed by Apple, Google, Samsung, and the CSA, allowing public-key zero trust mobile access using the same trust model as LEAF Verified physical cards.
LEAF credentials are built on an open standard, meaning the same card works with readers from multiple manufacturers. HID iCLASS SE and SEOS credentials are proprietary formats that only work with HID readers. LEAF also offers a public-key credential tier (LEAF Verified), which removes shared secrets from the credential entirely, a security model proprietary symmetric platforms aren't built to support.
Absolutely. Our Universal, Enterprise, and Verified credentials all use the same LEAF data format and can coexist in the same facility on the same reader infrastructure. Many organizations start with Universal for general population access and deploy Verified for high-security zones, all on the same readers.
Under normal daily use, a physical smart card will last well beyond 10 years. Wavelynx credentials built on the LEAF standard use NXP MIFARE DESFire EV3 and MIFARE DUOX silicon. NXP rates DESFire EV3 at 1,000,000 write cycles (typical) with 25-year data retention. The underlying cryptographic standards (AES, ECC P-256) are expected to remain secure for decades.
It means the technical specifications behind LEAF credentials are public. Any reader manufacturer or access control (PACS) vendor can build products that work with them, not just Wavelynx. The standard itself is governed by the LEAF Community, not by any single company. So if Wavelynx were no longer around, your credentials would still work with any LEAF-compatible reader on the market. Your investment is protected by the standard itself, not by a relationship with one vendor.